About
A practitioner to guide you.
Fredrik Lindstrom
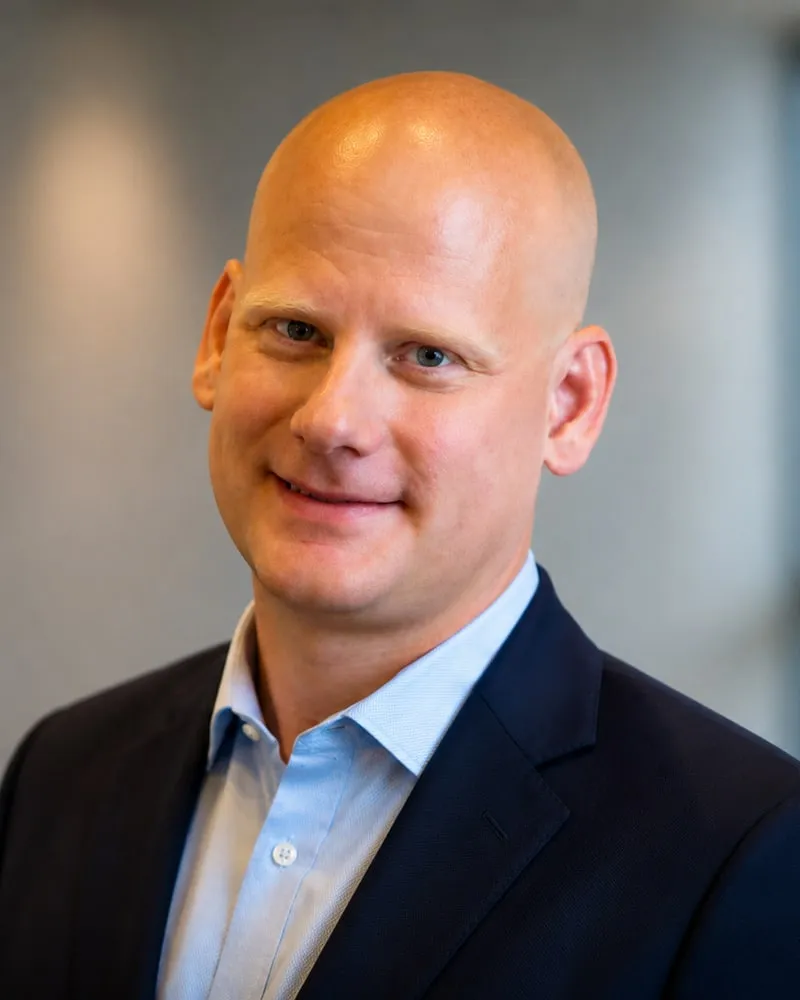
For 25 years I built and scaled technology-services businesses before turning that experience into board-level guidance on AI and cyber risk. I integrate governance into operations, so compliance comes as a result of how the business runs. Built in, not bolted on.
I spent nearly six years at Check Point Software, first as global head of professional services and then running global services sales. Over that stretch the services portfolio grew from $55M to $165M across 75 countries, and I built the managed security business from zero to more than $80M in three years. Before that, five years in CIO Advisory at KPMG, including an interim CIO seat through a bankruptcy reconstruction and divestiture (300 people to 50, about 80% of the cost out) and six months as interim CISO at a private-equity firm. Earlier, at Accuvant, I built a practice from six engineers and $1.5M to 40 engineers and roughly $26M. I have been the operator a board was holding accountable. That is most of why I am useful to one now.
The AI work at Check Point shipped. I defined the problems, architected the systems and led the engineering on four that run in production: a white-space engine that scans roughly 20,000 opportunities a month, a briefing pipeline that prepares more than 200 customer meetings a week, statements of work drafted from call transcripts, and AI practice scenarios for sales training. I also launched an AI security consulting practice (risk assessments, red teaming, adversarial testing of LLM and RAG systems) that delivered 100+ engagements in its first six months.
Since January 2026 I have run an independent practice in AI governance, cybersecurity and services. Two seats predate it. I have held the security and technology seat at a six-person regulated accounting practice since 2020, part-time, same client; it is the engagement that taught me what the fractional model is. And since August 2026 I have sat on the advisory board of a UK AI company that sells through private-equity funds into their portfolio companies.
The focus now is what comes next: artificial intelligence as a class of risk that boards have not yet learned to oversee, and that most enterprises are deploying faster than their governance can keep up with. I have watched this pattern before — cloud, mobile, data, now AI. The companies that build governance in parallel with deployment win. The ones that wait for the regulator pay twice. And this time there is no single regulator to wait for. The EU AI Act phases in through 2027, enforced across national competent authorities, market-surveillance bodies, notified bodies, and the EU AI Office, layered on top of the GDPR regulators already in place. Multi-agency, multi-jurisdiction, multi-year. That is the part most boards underestimate.
I write here for a specific audience: board directors, senior executives, and the technology leaders who advise them. The pieces are longer than a LinkedIn post and shorter than a consulting deliverable, built to give a busy reader the framing they need before their next governance review. The monthly Governance Memo collects the throughline.
Alongside the writing, I host Promise & Risk of AI, an educational YouTube channel built to cut through the hype and the fear-mongering. Every episode covers both the genuine benefit of an AI capability and the real risk attached to it, because the honest answer almost always sits between the people selling salvation and the people selling panic.
Credentials
- Certifications
- ISACA Advanced in AI Security Management (AAISM) · CISSP · CISM · CISA · PMP
- Education
- MBA, Rollins College · B.Sc. Computer Science, KTH Royal Institute of Technology, Stockholm
- Published in
- CIO.com · CIOReview · CRN — on AI risk, Zero Trust, and technology-services transformation
Areas of focus
AI Governance
Not a binder produced for the audit. I turn frameworks like the NIST AI Risk Management Framework and the EU AI Act into oversight boards can actually run, so compliance becomes a byproduct of how AI gets built and deployed. Committee design and charters where they earn their place, and dashboards that keep AI risk visible between meetings.
Cybersecurity Strategy
25 years of practitioner experience across enterprise security programs, vendor evaluation, and breach response. The core question I keep coming back to: where does the technical risk meet the fiduciary duty, and is the board seeing both sides clearly?
Enterprise AI Adoption
The integration paradox — the gap between what AI can do in a demo and what it does in a production environment with legacy systems, real workflows, and human oversight. Most enterprise AI failures are governance failures, not capability failures.
Board & Advisory
I work selectively with boards and senior leadership teams on AI governance design, security committee formation, and the literacy that directors need to ask better questions. If your committee meets next quarter and AI is on the agenda, that is the right time to be in touch.